-
Where this checklist works best
-
The six-step checklist
-
1. Define the answer to Okki Go vs Artisan AI before the demo
-
2. Audit what permissions does Okki Go require on LinkedIn, email, and CRM
-
3. Check intent data freshness before you build an email campaign around it
-
4. What should revenue operations teams evaluate in API email verification documentation
-
5. Run a low-volume staged launch before the full email campaign
-
6. Write the rollback plan before you accept the invitation
-
1. Define the answer to Okki Go vs Artisan AI before the demo
Real talk: six years of handling GTM tooling evaluations has taught me an uncomfortable lesson. Most AI SDR failures happen before the first email is sent. It took me three years, two bad vendor selections, and roughly $28,000 in wasted budget to understand that permission scopes, intent-data freshness, and API verification semantics matter more than a demo.
This is the checklist I now give my team before we approve any AI sales prospecting platform. It applies whether we are comparing Okki Go vs Artisan AI, answering a security question about permissions, or deciding if an API email verification documentation is good enough to support an email campaign.
Where this checklist works best
Use this checklist at two moments. First, when a vendor demo has ended and the platform is technically shortlisted. Second, before security and RevOps sign off on the actual account permissions. If you are still at the Okki Go vs Artisan AI stage and using comparison pages as your main research, this checklist will give you better questions to ask in the next demo.
There are six steps. The checklist assumes you are responsible for connecting an AI SDR to real LinkedIn accounts, real email inboxes, and a real campaign. That is where theory ends.
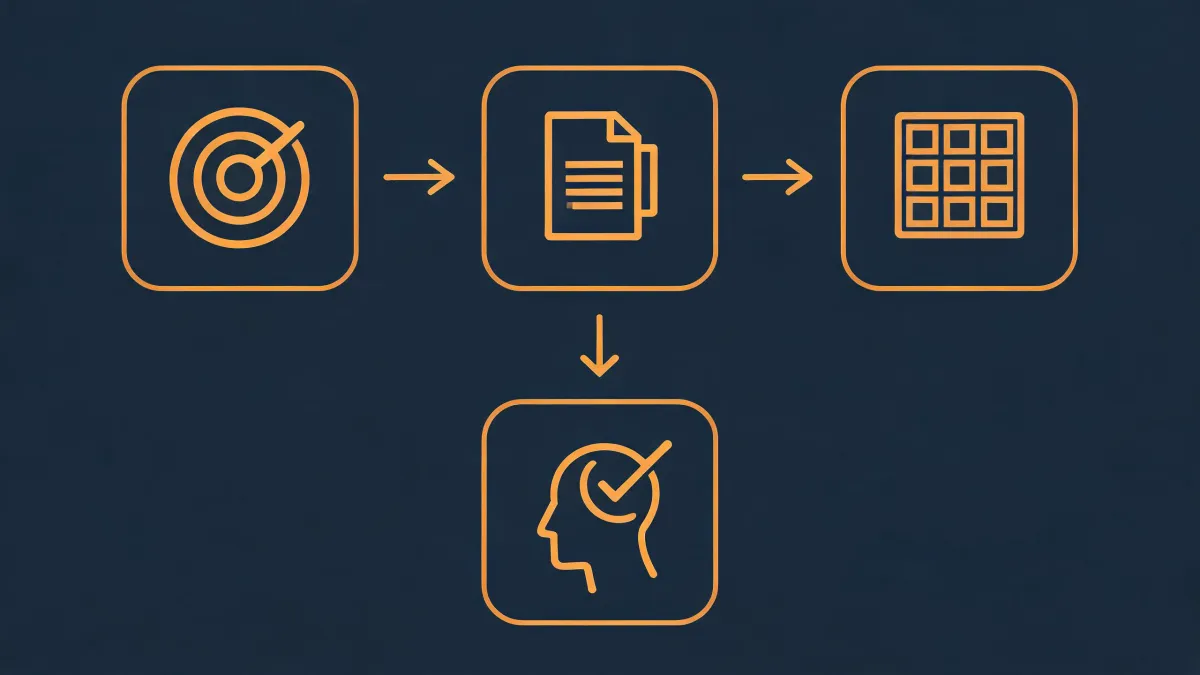
The six-step checklist
1. Define the answer to Okki Go vs Artisan AI before the demo
Search results for Okki Go vs Artisan AI are usually feature comparisons. Feature lists tell you what exists, not how the product behaves when your data is messy or your compliance team gets involved.
Before I compare two platforms, I write down the exact outbound motion we are trying to improve. Are we automating follow-up on inbound leads? Starting cold conversations in a new market? Reviving old pipeline? The best AI SDR for one use case can be the wrong one for another.
My rule now is simple: compare outcomes, not adjectives. For each vendor, answer four questions:
- Which parts of the email campaign workflow are automated, and which parts require human approval?
- What triggers a prospect to move from research to outreach?
- How does intent data influence the sequence, and when does it expire?
- Does the platform verify and enrich contacts before the AI agent contacts them, or does it hand the SDR an unvalidated list?
Demos are selected for optimism. The real test is what the platform does with bad data, missing fields, and unusual email addresses.
2. Audit what permissions does Okki Go require on LinkedIn, email, and CRM
Before I approve anything, I ask: what permissions does Okki Go require? If a vendor cannot answer that with a clear permission list, that is already a red flag.
Okki Go connects to LinkedIn, email, and sometimes a CRM. The exact permission list depends on the connectors you activate, but the current integration in April 2026 groups access into four areas:
- LinkedIn access: reading profile and Sales Navigator context, and sending connection requests or messages when the sequence is activated by a user.
- Email access: OAuth access to your sending account to create, send, and track sequences. This should not require IMAP credentials or a mailbox password.
- CRM access: read access to accounts and contacts, plus write access to create activities or leads. Delete access should not be part of an SDR integration.
- Browser enrichment: if the Okki Go extension is used for LinkedIn prospecting, it reads page context on profile and search pages. It should not be reading unrelated browsing history.
This is not meant to replace the actual documentation review. The important thing is what you should look for: narrow OAuth scopes that match the workflow. If the vendor asks for full mailbox access or broad CRM admin permissions, stop the evaluation and ask why.
3. Check intent data freshness before you build an email campaign around it
Intent data was the reason I bought my first AI SDR. I saw 18,000 accounts labeled as in market and assumed that meant they were ready to talk. The campaign produced almost no meaningful meetings. Why? The intent signals were old, they were account-level, and many of those contacts had never been email verified.
That mistake taught me a simple rule: intent data tells an agent where to look, not who to email. The person still needs to fit your ICP, exist in a verified contact record, and not be on a suppression list.
When you evaluate intent data, ask the vendor to explain:
- What the signal actually measures. Is it content consumption, search behavior, competitor research, or something else?
- When the signal happened. A timestamp matters more than a label that says high intent.
- Whether it can be matched to a person or only to an account. Person-level intent is more useful for personalized email campaigns.
- How the platform handles do-not-contact and suppression lists before triggering outreach.
If a platform says it has integrated intent data, ask what happens when the intent score decays. Does the campaign pause, or does it keep sending based on a stale signal? That answer will tell you more than the sales deck.
4. What should revenue operations teams evaluate in API email verification documentation
The worst part of my failed campaign was not the email copy. It was the false confidence from a verification report that labeled bad records as valid. Here is the thing: an email verification API can say valid while only meaning the address has a proper format.
RevOps teams often do not write code, but they can still read API email verification documentation. In fact, they should. The questions I now keep in our evaluation checklist are:
- What does the status field actually mean? Does valid mean deliverable, syntax only, or that the mailbox accepted the message?
- How are catch-all domains classified? A record with a catch-all status is not the same as a confirmed valid address. It should be labeled risky or unknown.
- What reason codes are returned? Can you tell whether an email is invalid, disposable, role-based, or temporarily retryable?
- How are role-based addresses handled? Emails like info@ or contact@ should not be sent through an outbound SDR workflow without a clear decision.
- What are the webhook and response-time patterns? If you plan to verify leads at enrichment time, the API needs to be fast enough for that workflow.
- What data is logged and retained? Email addresses are personal data. Your security team will want to know what happens to them after verification.
Why does this matter? Because a campaign can look fine in a dashboard and still have a hidden list-quality problem. The API documentation is where those problems become visible.
5. Run a low-volume staged launch before the full email campaign
Once the tool is approved, do not switch on the entire outbound motion in one afternoon. That is how permission mistakes and data mistakes turn into deliverability problems.
I now require a staged rollout before any full email campaign. Start with a small number of accounts that match your ICP. Send a limited number of emails, and require human review of the first few messages before automation takes over. Monitor hard bounces, spam complaints, and the queue behavior. If something looks wrong, you want to find it before the campaign reaches thousands of contacts.
This also tests the human-in-the-loop part of the platform. An AI SDR should be able to research, enrich, and draft. But when an email is flagged as risky or a prospect replies with a compliance question, there needs to be a human who can step in.
6. Write the rollback plan before you accept the invitation
Before you sign anything, ask one more question: if this platform does not work, how do we disconnect it safely? The answer should include exporting contacts, sequences, and engagement histories. It should also explain how API keys are revoked and what happens to any data already synced into your CRM.
I have seen too many teams evaluate a new tool as if cancellation is just a billing question. It is not. The rollback plan is part of the evaluation. If a vendor avoids the question or makes the data export sound complicated, treat that as a warning sign.
Bottom line: Okki Go vs Artisan AI is the type of comparison that starts in search results, but the real evaluation belongs in documentation. The expensive questions are about OAuth scopes, intent freshness, API status codes, and rollback paths. If you use this checklist, you are not choosing a tool because of a demo. You are choosing it because you know what it can safely do with your data.